Exkurs und Aufgabe: SQL-Injection
Completion requirements
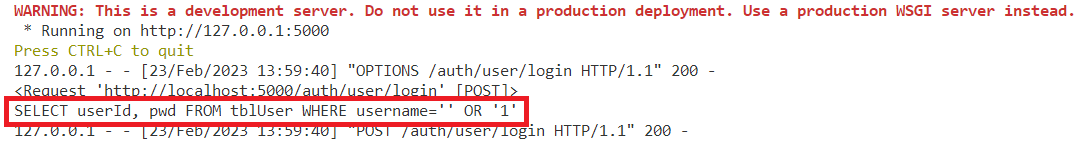
Ausgabe der injektierten SQL-Anweisung
(Danke geht an Semih Bachmann FI0J)
Suchen Sie weitere Angriffsmöglichkeiten mit SQL-Injection und Lösungswege, mit denen diese abgewehrt werden können.
Das Projekt SimpleAuthService auf Github: https://github.com/ateachment/SimpleAuthService/tree/develop-db
ist noch anfällig für eine SQL-Injection! Die Eingabe:
' OR '1
im Eingabefeld Username erübrigt dessen Eingabe.
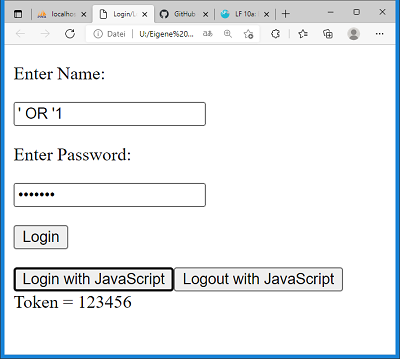
Eingabemaske mit SQL-Fragment als Eingabe
Das heißt, bei der Anmeldung wird hier in diesem Projekt das Kennwort aller in der Datenbank befindlichen Benutzer überprüft:
Um das zu verdeutlichen wird die zusammengesetzte Abfrage mit der Injection in Zeile 40 ausgegeben:
21 22 23 24 25 26 27 28 29 30 31 32 33 34 35 36 37 38 39 40 41 42 43 44 45 46 47 48 49 50 51 52 53 54 55 56 57 58 59 | ... @app.route('/auth/user/login', methods=['POST']) def loginUser(): content_type = request.headers.get('Content-Type') if content_type == 'application/json': print(request) username = request.json['username'] password = request.json['password'] elif (content_type == 'application/x-www-form-urlencoded'): # regular html form data username = request.form['username'] password = request.form['password'] else: return 'Content-Type not supported: ' + content_type, 400 # Bad request db1 = db.Db() ph = PasswordHasher() hashedPW = ph.hash(str(password)) query = "SELECT userId, pwd FROM tblUser WHERE username='%s'" %(username) print(query) result = db1.execute(query) if(result): for row in result: # more than one user with this username possible try: # verify hashed password fail -> throws exception if ph.verify(row[1], password) == True: # check hashed password userId = row[0] token = generateToken() query = "UPDATE tblUser SET token = '%s' WHERE userID=%d" %(token, userId) result = db1.execute(query) db1.commit() # actually execute return json.dumps({ "token": token }) # 200 OK except: pass return json.dumps({ "token": "-1" }), 403 # 403 forbidden - wrong password else: return json.dumps({ "token": "-1" }), 403 # 403 forbidden - no user with this username del db1 # close db connection ... |